01
Pre-Compromise Focus
Detection after the fact is damage control. We instrument for visibility before incidents occur, because finding the adversary during their reconnaissance phase is the only win that matters.
NorthQuinn was founded on the reality that most organizations are compromised long before they know it. We exist to change that equation.
Across Mandiant’s 2025 investigations, attackers went undetected for a median of 14 days, and a median hides the long tail of intrusions built to stay quiet far longer. By the time most organizations detect a breach, the attacker has mapped the environment, established persistence, and exfiltrated what they came for. NorthQuinn was built to break that pattern.
We combine autonomous threat detection technology with deep operational expertise to give defenders the visibility they have always needed but rarely had. Our flagship platform, AVERY, was designed from first principles around the assumption that advanced actors are already present, and that the goal is finding them before they find what they are looking for.
Detection after the fact is damage control. We instrument for visibility before incidents occur, because finding the adversary during their reconnaissance phase is the only win that matters.
Alert fatigue kills SOC effectiveness. Every detection capability we build is engineered to surface actionable intelligence, not generate noise your team has to filter through at 2 AM.
We explain every detection, every tuning decision, and every recommendation in plain language. Your security program should not be a black box, even when the technology inside it is sophisticated.
Security stacks built on shortcuts fail under pressure. We build for adversarial conditions from day one, every integration, every rule, every deployment decision made with real attack scenarios in mind.
TTPs change. Threat actors adapt. A static ruleset is a liability. We operationalize live threat intelligence so your defenses evolve with the threat landscape, not six months behind it.
NorthQuinn is principal-led. Every engagement is owned at the highest level of the firm, with direct accountability to the client from start to finish.
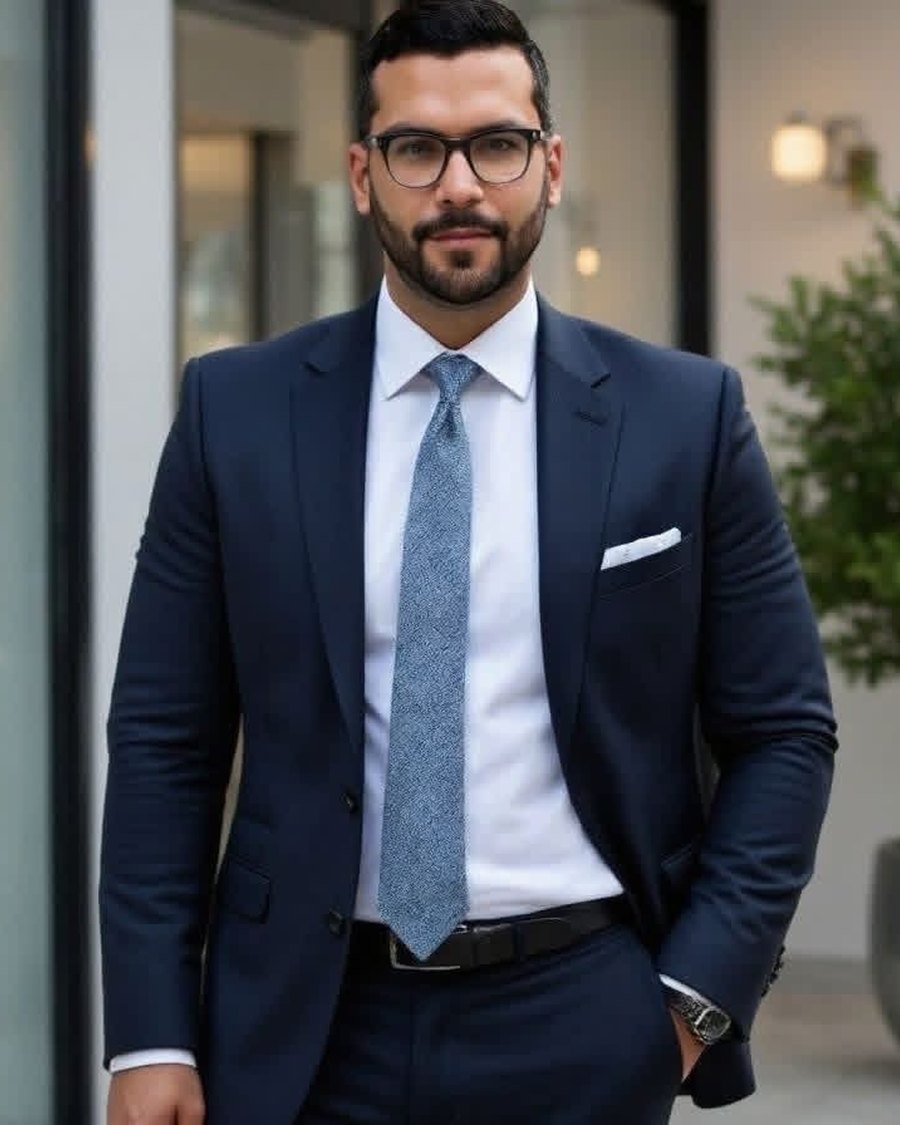
Founded by Angel Gonzalez Gines, Founder & CEO.
Angel Gonzalez Gines is the founder and CEO of NorthQuinn and the architect of AVERY, a behavioral threat intelligence platform for federal, IC, and defense teams. He brings over thirteen years of experience across cybersecurity, IT infrastructure, and financial services, operating across enterprise and government environments in the United States before founding NorthQuinn.
His technical background spans the full defensive stack, from network monitoring and endpoint detection to threat intelligence integration and SOC architecture. AVERY, the autonomous detection platform he designed, reflects years of thinking about what pre-compromise visibility actually requires at the architecture level.
NorthQuinn did not start with a pitch deck. It started with a pattern recognition problem, watching organizations get compromised by actors who had been inside their networks for months, operating undetected because the detection capabilities those organizations had were never designed for the adversary they were actually facing.
AVERY started as an architecture document in 2024, built around a set of non-negotiables: pre-compromise focus, intelligence integration, and high-fidelity detection over alert volume. Everything since then has been building toward the platform those principles required.
The original architecture document establishes the philosophical and technical foundation: intelligence platform, pre-compromise focus, adversary-centric design. Non-negotiables locked before any stack decisions.
The defensive stack is finalized around modern open-source tooling. AVERY's detection architecture is locked and initial instrumentation begins. Components move from design to active build.
NorthQuinn is formally incorporated as a Delaware C Corporation, with the legal structure in place to serve government, IC, and enterprise clients. Public open-source tooling launches on GitHub.
The detection engine and enrichment pipeline are in active development. NorthQuinn is accepting its first strategic partnerships and client engagements.
NorthQuinn publishes the research behind its detection approach, the open-source tools that implement parts of it, and the measured limits of both. Every paper goes through responsible disclosure before release and says plainly where its method does not work.
NorthQuinn is an early-stage company with a working thesis, published research, and a platform in development. We’re looking for a small number of experienced people who want to own a hard part of it from the beginning.
What matters more than titles: you have shipped something that worked under real conditions, you would rather measure than assert, and you are comfortable with ambiguity.
The work is real and so are the unknowns. Responsibilities are broad, structure is light, and much of what exists will be shaped by the first people who join. Roles, commitment, and terms are worked out directly with the people who fit, not through a job listing.
Write to info@northquinn.com or use the contact form and choose “Founding Team.” Tell us what you have built, which problem above you would want to own, and link to work we can look at: code, writing, or research.
Researchers interested in collaborating on these questions can choose “Research Collaboration.”
Whether you need a platform demonstration, an incident response, or a full SOC buildout, it starts with a conversation.
Get In Touch